v3.18.0
What’s new
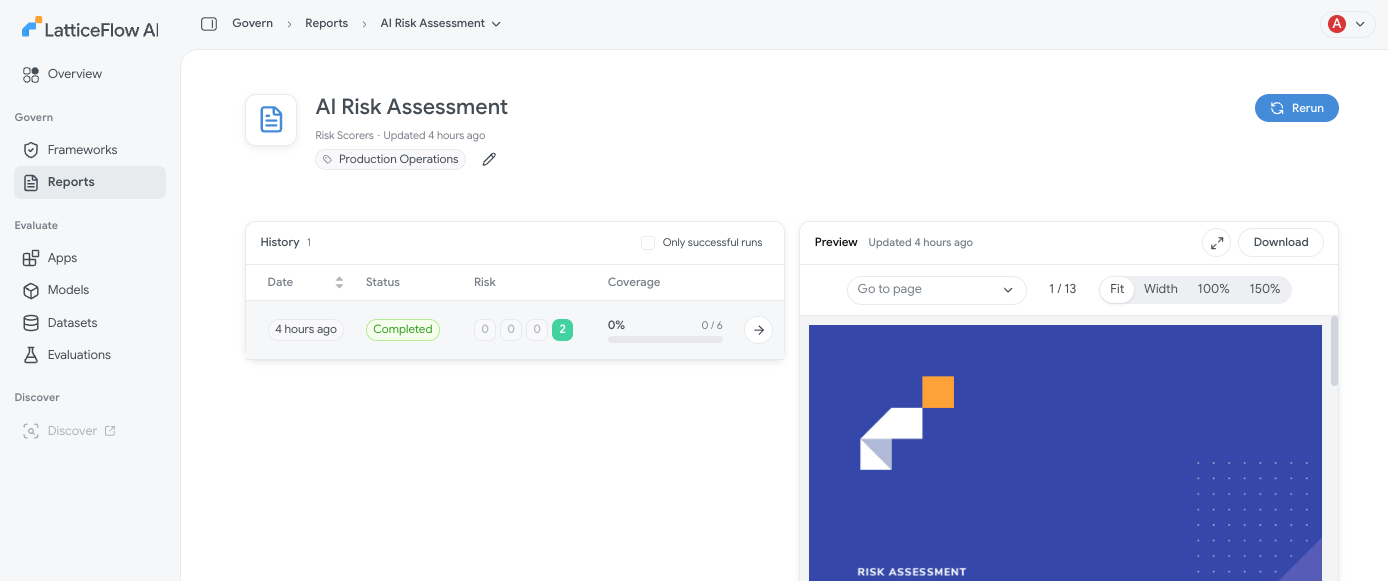
- Risk reports: A new Reports page under Govern generates a PDF risk report for an AI app based on the frameworks you select, and keeps each report’s run history.
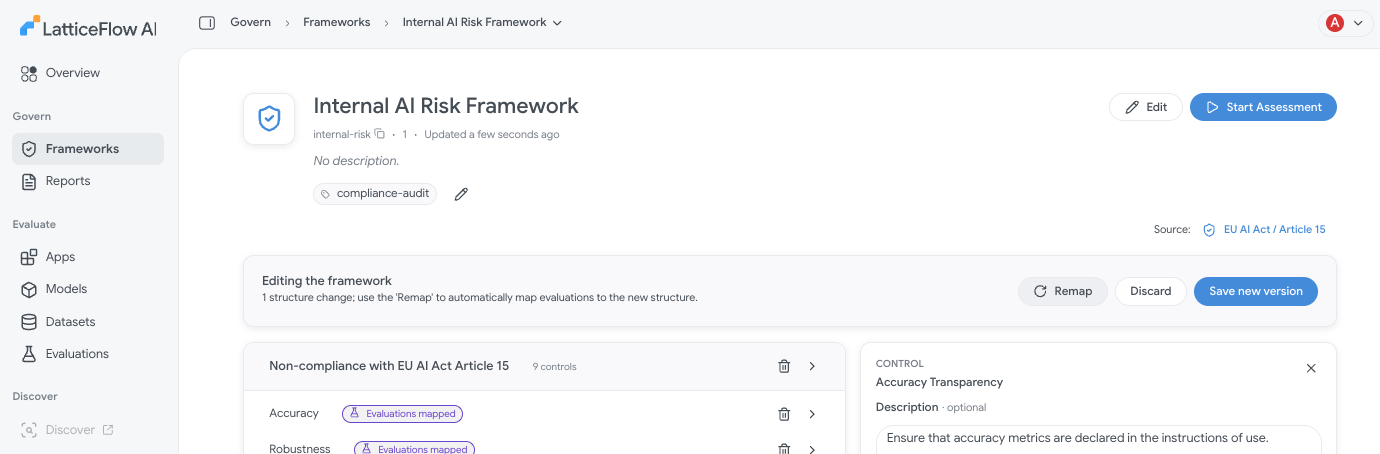
- Automatic framework to evaluation mapping: The framework editor can now suggest the evaluations that cover each risk, sub-risk or control, and you can review the suggestions before you accept them. The same mapping is available from the CLI with
lf automate framework-mapping.
New Atlas frameworks: AI Atlas now includes the OWASP Top 10 for LLM Applications - 2026 revision, China’s TC260 AI Safety Governance Framework 3.0 and Colorado’s Automated Decision-Making Technology law (SB 26-189).
New Atlas evaluations: New evaluations cover sycophancy, invisible text injection, unqualified advice in sensitive domains, summarization accuracy, general QA, and red-teaming.
Improvements
New navigation: The UI has a collapsible sidebar grouped into Govern and Evaluate, breadcrumbs, and consistent page headers. In Settings, the API Key tab is now CLI and includes the CLI setup instructions, and Support is now About.
Less noisy CLI output:
lf initprints each pre-filled model key once instead of once per evaluation.lf export,lf set system-model,lf dump entitiesandlf init evalonly show the AI App context when they use it.
Bug fixes
- RAG citations were not shown in the evidence viewer.
- Custom code execution could stop working until restart if the sandbox orchestrator process died. The orchestrator now restarts automatically.
- The framework editor could show an outdated structure after the framework was updated from a file.
- Rerunning an evaluation no longer drops its repeatability and trials configuration.
Breaking changes
Risk scorers and policies must list evaluations: The
all_latestscope has been removed, and the scope’sscorer_keyandmetric_keyfields are gone. A scope now needs a non-emptyevaluation_keyslist (see Risk Scorer Scope). When you upgrade, risk scorers whose scope doesn’t list any evaluation keys are deleted.Risk domains moved from risk scorers to evaluations: Risk scorers no longer have a
domain. An evaluation’sdomainsnow lists its risk domains (e.g.cybersecurity), and the field that used to be calleddomains(e.g.finance) is nowindustries(see Evaluations reference). A risk score’s domains come from its evaluations, so a risk score can belong to several domains.